SecOps & Threat Telemetry Blueprint
Clean-Room Technical Deep Dive: Threat Telemetry, Spatial Analytics & SIEM Federation
Threat Telemetry & Geo Footprint Topology
Production Deployed
1. Business & Technical Context
Enterprise Security Operations Centers (SOCs) monitoring globally distributed server fleets face overwhelming alert noise and high-velocity packet influx. Traditional threat isolation required manual correlation between network telemetry logs and external threat intelligence feeds—a process taking 30 to 45 minutes per security incident. The challenge was building an automated telemetry pipeline to ingest line-rate network flows, isolate geolocation attack vectors, and correlate alerts in real-time.
2. Architectural Decisions & Trade-offs
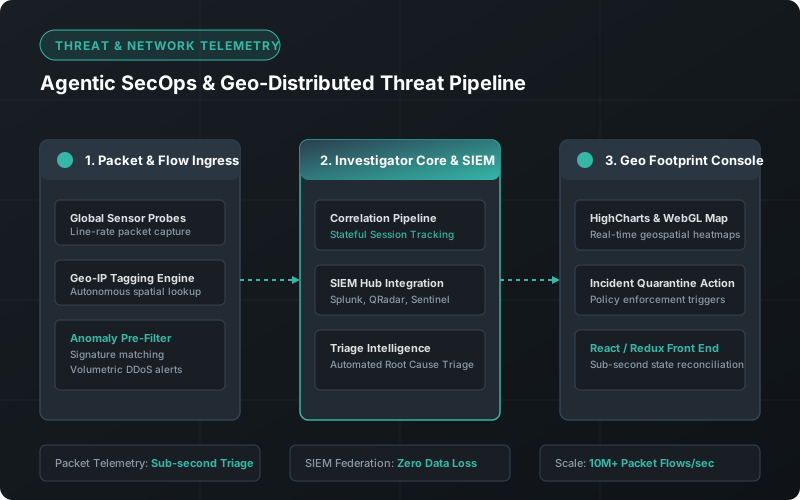
- Asynchronous Ingress & Spatial Tagging: Designed distributed sensor probe parsers streaming into a stateful correlation engine. Incoming packets are enriched at ingress with autonomous Geo-IP spatial attributes without blocking packet capture threads.
- SIEM Federation Hub: Standardized event schema normalization allowing bi-directional synchronization with Splunk, IBM QRadar, and Microsoft Sentinel, preventing vendor lock-in for enterprise clients.
- High-Density Visualization Layer: Replaced legacy server-rendered tables with React, Redux, and HighCharts, employing client-side spatial indexing for sub-second viewport re-rendering.
3. Engineering Challenges & Mitigations
- DOM Overload Under Volumetric Attacks: Network floods (DDoS) produce millions of log records. Implemented virtualized windowing and aggregated geospatial clustering, capping client memory footprint under 120MB.
- SIEM Ingestion Throttling: Mitigated downstream SIEM drop-outs using asynchronous backpressure queues and dynamic log severity throttling.
- Automated Policy & Regression Testing: Established end-to-end telemetry simulation testbeds utilizing WebdriverIO to guarantee zero behavioral degradation across critical releases.
4. Measurable Outcomes & Metrics
< 1s
Incident Triage Latency
10M+
Flows / Sec Processed
0%
Telemetry Packet Drop
Initiative Metadata
- Role: Senior Software Systems Architect
- Pod Scope: Core Systems & Threat Analytics
- Domain: Cybersecurity & Network Telemetry
- Stack: React, Redux, SIEM, HighCharts
- Platform: Omnis™ Cyber Investigator & Geo Map
Technical Leadership Discussion
Interested in high-throughput network architectures, spatial telemetry, or threat triage automation?
Initiate Executive Discussion